

How a 10-minute call cost a casino group $139 million
It is three years since the cyber hack of MGM Resorts which crippled their systems, close them $139 million, and saw the personal information of 37 million people end up on the Dark Web, and it all happened because of a 10-minute vishing phone call.

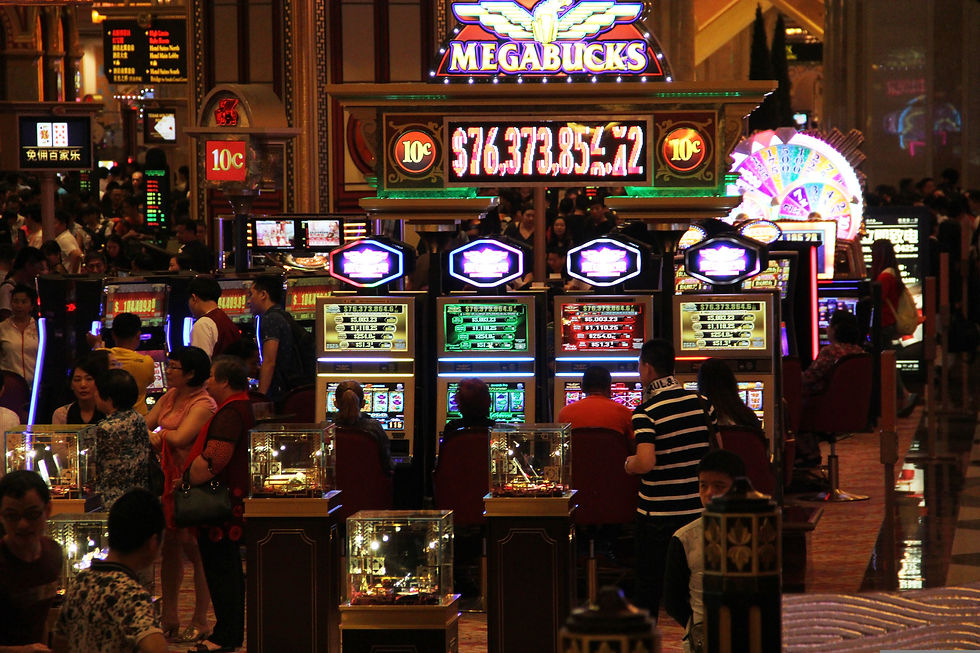
MGM Resorts include the MGM Grand, Bellagio, Mandalay Bay, Mirage and Luxor hotels and casinos in Las Vegas, but it also bosts locations in Atlantic City, Detroit and other sites outside of the United States such as China and Japan. In total, 30 properties were affected.
On September 9, 2023, members of hacker group Scattered Spider searched LinkedIn for MGM employees in order to find one which would have the role and credentials they would require to execute a successful hack. After locating one, they contacted MGM's help desk posing as the employee to obtain login credentials and supply a new password to them.
The Wall Street Journal reported: "The person on the line said they were an employee, but had forgotten their password...They gave some personal information over the phone. It all checked out."
Using that information, they gained administrator privileges, and deployed ransomware within the servers, which spread to thousands of machines.
These machines supported gaming machines, online reservation and hospitality systems, digital room keys, and websites. In additions, 6 terabytes of customer information was extracted, and used to pressure MGM into paying a ransom to stop the data being released online.
MGM refused to pay. In response, the personal information of 37 million people who had stayed at MGM Reports' hotels were dropped onto the Dark Web by Scattered Spider. This included full names, home addresses, phone numbers, email addresses, and dates of birth. It also included some customers' passport numbers, driver's licence numbers and social security details.
In the meantime, MGM shut down its own infrastructure. This meant:
Slot machines went offline
Online booking and reservations were closed
The MGM app became unavailable
Email systems were affected
ATMs went offline
Restaurant reservations were stopped
Hotel digital keys stopped working
This went on for ten days before MGM claimed things were working normally, but systems were reportedly being restored up to 25 days after the initial hack.
The financial and reputational damage to MGM Resorts was enormous. It lost $84 million in lost recenue, and spent $10 million for things like consultants, technology expertise and legal fees, and also settled a class action lawsuit brought by the victims for £45 million.
While this was a high-profile, highly-costly experience, there are lessons to take away for any business, as the initial access was procured by the hackers due to a little social media scouting and a quick phone call pretending to be an employee who had forgotten their login details.
More than 40% of help desk requests to IT service desks relate to password resets, and when it comes to larger companies, it's likely that the person asking for the password reset and the person performing it aren't known to each other. Couple that with how quickly IT desks have to turn over requests and move onto the next job, it is understandable how a good vishing attempt can slip through.


Comments